Threat actors use legitimate Bing redirect links in Google search ads to trick users into downloading malware disguised as the Claude AI installer.
Key points
- Attackers inject Bing redirect URLs into Google Ads to mask malicious destinations.
- The campaign distributes ClickFix malware disguised as official Claude installers.
- The scheme relies on user trust in search results and familiar brand names.
Cybercriminals are deploying a new distribution method for ClickFix malware by hiding malicious links behind legitimate Bing search redirects within Google Ads. This technique tricks users into believing they are visiting a safe destination while delivering harmful software.
What happened
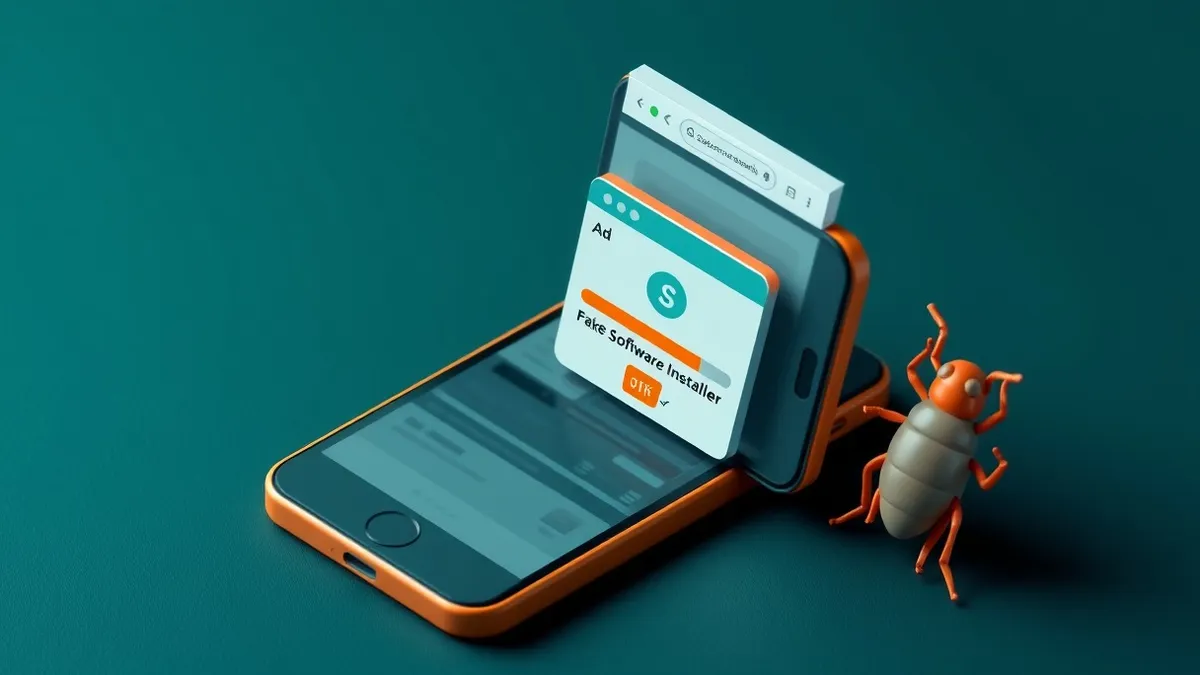
Hackers are currently abusing legitimate Bing search-result redirect mechanisms as click URLs in Google search advertisements, according to BleepingComputer. These ads direct unsuspecting users to fake installers that mimic the popular Claude artificial intelligence platform. Once executed, these fake installers deliver ClickFix malware to the victim's device. The attackers leverage the trusted appearance of Bing redirects to bypass initial suspicion.
Why it matters
This campaign demonstrates how threat actors exploit trust in major technology platforms to distribute malware. Users often assume that ads appearing on Google or redirects from Bing are safe, creating a false sense of security. The use of a popular brand like Claude increases the likelihood that victims will download the file without verification. This method makes traditional URL inspection less effective because the initial link appears legitimate. The ClickFix malware poses a significant risk to user data and system integrity.
The fix
No specific software patch or vendor update has been confirmed for this distribution method yet. Users must rely on vigilant behavior and verification practices to avoid infection. Checking the actual destination URL before clicking is essential. Downloading software only from official vendor websites remains the safest approach.
What to do and how to stay safe: ClickFix
- Verify the final destination URL by hovering over ad links before clicking to see the true address.
- Download Claude and other AI tools only from Anthropic's official website or trusted app stores.
- Use browser extensions that block intrusive ads and known malicious domains to reduce exposure.
- Keep your operating system and security software updated to detect and block known malware variants.
Step-by-step guide: Social Engineering Risks and Protection for Small Businesses
General security guidance from the Crypt Weekly newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
How do hackers use Bing redirects in Google Ads?
They use legitimate Bing redirect links as the click URL in Google ads to mask the final malicious destination from users.
What malware is being distributed in this campaign?
The campaign distributes ClickFix malware disguised as fake Claude AI installers.
Is there a patch for this issue?
No patch has been confirmed because this is a distribution technique using ads, not a software vulnerability in Claude or Bing.