Privacy & Policy
Removing People-Search Data: Real Benefits and Hard Limits
Clearing your personal records from broker sites stops automated harvesting temporarily, but public government registries regenerate the profiles continuously.
The security desk for defenders
Reference guides from the Crypt Weekly newsroom. They explain the ideas behind the headlines and are reviewed when the facts change.
Clearing your personal records from broker sites stops automated harvesting temporarily, but public government registries regenerate the profiles continuously.
Public Wi-Fi finder apps harvest and sell your location history while promising to keep your mobile data connection secure.
Revoking location permissions on social media fixes nothing if historical geotags already map your daily routines.
Adversarial patterns and infrared frames fail when surrounding cameras use gait analysis, multi-angle stitching, or visible light sensors.
Cookies live inside user browsers while sessions reside on remote servers, creating a fundamental split in trust and data storage.
RSA encryption remains secure because factoring massive numbers takes more energy than computers can manage.
Strict authentication rules often force predictable user behavior that weakest overall digital defense systems across modern networks.
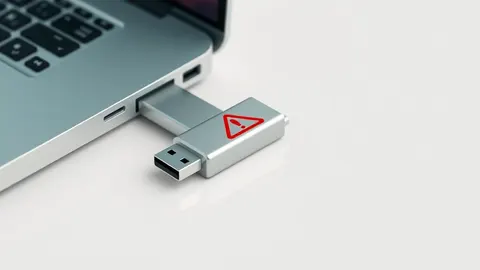
Universal Serial Bus thumb drives bypass network perimeter defenses by executing code directly on host operating systems.
Modern smartphones isolate applications using sandboxing, yet local hardware access and wireless eavesdropping still bypass default defenses.

Most critical vulnerabilities hide in transitive dependencies that your build tools do not explicitly list or track during standard development cycles.
Container escapes succeed not by breaking the container walls, but by exploiting the shared kernel that runs underneath them.
Regulatory approval does not equal security validation, and air-gapping fails when maintenance staff connect diagnostic tools to the network.
FortiGate flaws often stem from complex code interactions that turn security gateways into entry points for unauthorized access.
Compiler flags and static analysis catch most null pointer dereferences before runtime, but they miss logic errors that require defensive programming patterns.
Most threat models fail because they map data incorrectly and ignore the human operators who maintain the system in production.
Segmentation stops lateral movement faster than patching because it limits the blast radius of any zero-day exploit in your network infrastructure.
Emergency patches often bypass standard controls, creating a hidden audit gap that allows misconfigurations to persist long after the security flaw is closed.
PHP vulnerabilities arise when code treats untrusted input as executable instructions, turning standard web interactions into remote command execution opportunities.
Free themes often contain hidden backdoors that bypass standard security checks, while outdated dependencies create silent entry points for attackers.
Your medical records can be hijacked to claim insurance benefits, creating debt and errors that distort your actual health history.
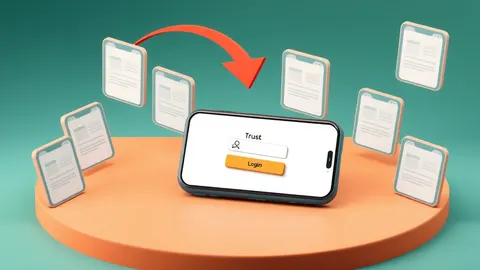
Attackers steal access tokens by tricking you into approving legitimate requests on fake pages that mirror real apps.
Privacy policies are legal disclaimers about data processing, not technical blueprints for security or guarantees of personal anonymity.
Frequent password changes force users to choose weaker secrets and reuse them, creating larger attack surfaces for credential stuffing and phishing campaigns.
Tax identity theft often stems from overlooked administrative gaps like unmonitored mail and weak secondary authentication, not just stolen passwords.